ACL
Just testing with ACLs
Topology:
Topology:
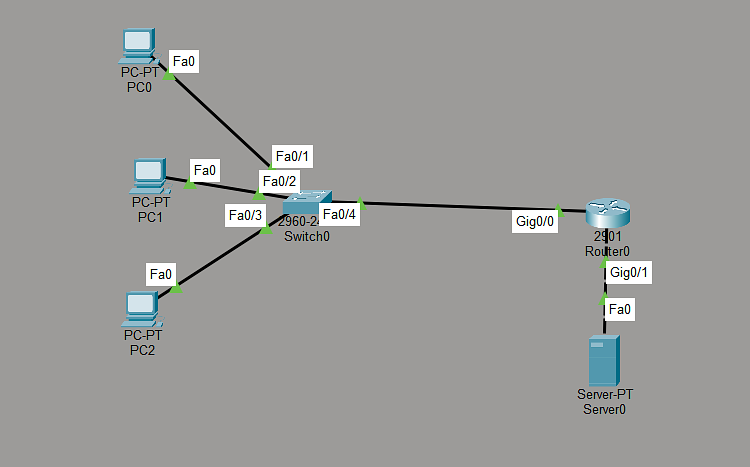
R1
Interface IP-Address OK? Method Status Protocol
GigabitEthernet0/0 192.168.1.1 YES manual up up
GigabitEthernet0/1 192.168.2.1 YES manual up up
Vlan1 unassigned YES unset administratively down down
Creating a standard ACL:
enable
conf t
access-list 10 deny host 192.168.1.20
access-list 10 permit any
end
Applying the ACL to R1's g0/1 int
en
conf t
int g0/1
ip access-group 10 out
end
Ping from PC0:
C:\>ping 192.168.2.10
Pinging 192.168.2.10 with 32 bytes of data:
Reply from 192.168.2.10: bytes=32 time<1ms TTL=127
Reply from 192.168.2.10: bytes=32 time<1ms TTL=127
Reply from 192.168.2.10: bytes=32 time<1ms TTL=127
Reply from 192.168.2.10: bytes=32 time=1ms TTL=127
Ping statistics for 192.168.2.10:
Packets: Sent = 4, Received = 4, Lost = 0 (0% loss),
Approximate round trip times in milli-seconds:
Minimum = 0ms, Maximum = 1ms, Average = 0ms
Ping from PC1:
C:\>ping 192.168.2.10
Pinging 192.168.2.10 with 32 bytes of data:
Reply from 192.168.1.1: Destination host unreachable.
Reply from 192.168.1.1: Destination host unreachable.
Reply from 192.168.1.1: Destination host unreachable.
Reply from 192.168.1.1: Destination host unreachable.
Ping statistics for 192.168.2.10:
Packets: Sent = 4, Received = 0, Lost = 4 (100% loss),